Writing
Every post, newest first. Security research write-ups, longer pieces on firmware and the software supply chain, and things I build.
2026
If You Wanted to Watch a Country
We pulled MAX apart and read the code: the surveillance machine you could build on top of it, and how little of it we had to make up.
A one-tap token drain in Unstoppable Wallet, and the $20 bug bounty it earned
One blind tap empties a token in this crypto wallet: confirmed by its own makers, since fixed, and settled with a $20 bug-bounty payout.
A Zero-Day in Android’s Wi-Fi Direct: Any App Can Steal Your Password, Zero Permissions
Any app can flip one flag and read your live Wi-Fi Direct password, zero permissions, no prompt.
A Zero-Day Screen Hijack in Android’s Tap-to-Pay: The Grant That Never Expires
Any app that was ever your tap-to-pay handler keeps a permanent, background screen-hijack power, even after a clean logout.
Part 2: Risks and Vulnerabilities in Hardware Systems
What a Samsung Galaxy S25 Ultra trusts without asking
A Zero-Day That Lets Any App Rewrite What Your Screen Reader Says
No permission, no prompt: any app can rewrite what TalkBack reads aloud to a blind user, System UI included.
Your DMV Can Trigger an Out-of-Bounds Read Inside Google Wallet
One ordinary photo from your driver’s-license issuer, and Google Wallet reads past its buffer.
A Zero-Day in Android’s On-Device AI: Any App Can Open a Door to Gemini Nano
Any app can grant itself one ordinary-looking permission and open a live door to Gemini Nano, no prompt, no consent screen.
A Zero-Day in Google’s Confidential Computing: Your Phone Can Be Fooled Into Trusting a Fake Enclave
A forged proof passes Google’s enclave attestation: the check binding it to the real program is silently skipped.
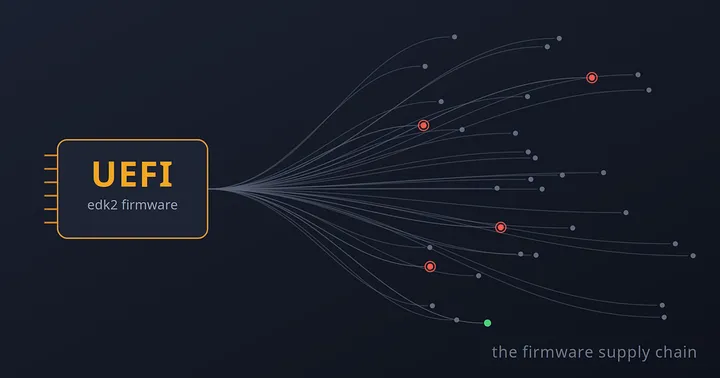
Making Firmware Verifiable, Not Just Signed
My journey into the UEFI firmware supply chain: abandoned dependencies, code you can’t verify, and the open-source tooling I built so firmware can prove itself.
2025
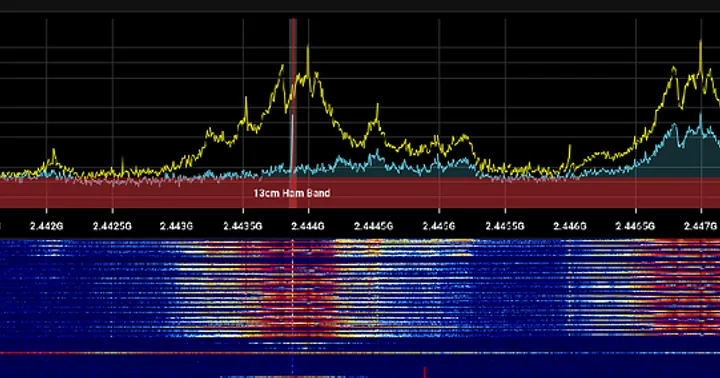
Inclusive Hacking: Ride-On Cars to Empower Children with Disabilities
GoBabyGo IL Investigates Full-Control Wireless Adaptations for Children with Disabilities
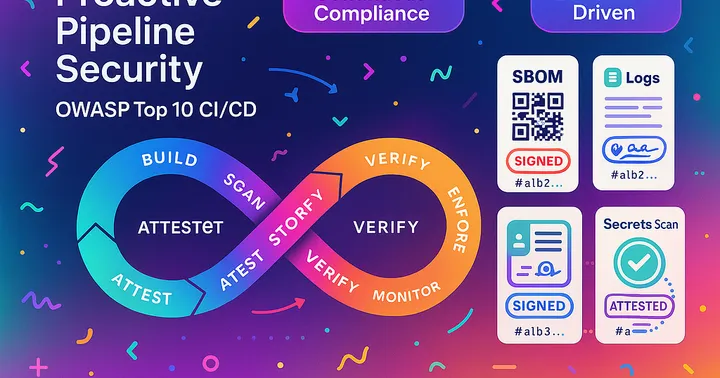
Proactive Pipeline Security: Applying the OWASP Top 10 CI/CD Risks with Scribe
Turn OWASP Top 10 risks into automated, auditable controls
SLSA Compliance at Scale: Provenance Generation with Scribe
From Logs to Proof: Evidence-Centric SLSA Compliance at Scale
Achieving SP 800-190 Continuous Container Compliance with Scribe Security
A hands-on guide to enforcing secure container policies at every pull request and release.
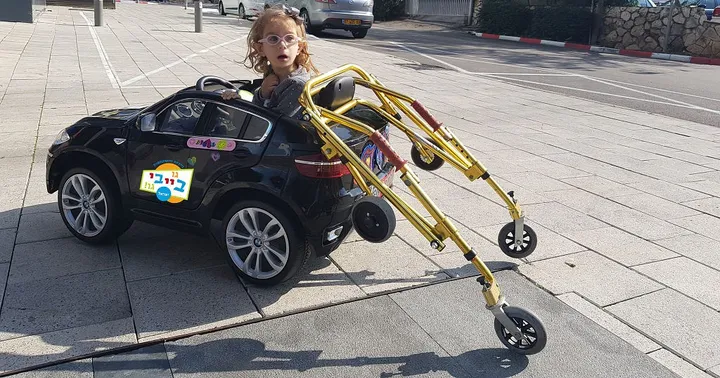
Adapting Cars for Children with Disabilities: The GoBabyGo IL Core Build Kit
Simple, Accessible Solutions for Customizing Cars for Children with Disabilities
2024
2023
CycloneDX Dependency Graphs
Enhancing Security, Policy Enforcement, and Beyond
From Chaos to Clarity: How to Secure Your Supply Chain with Attestations
A Look at a Continuous Compliance Platform
Risks and Vulnerabilities in Hardware Systems: A Case for Greater Awareness
New Linux Kernel Security Risks: Four Zero-Day Vulnerabilities Revealed